{
“@context”: “https://schema.org”,
“@type”: “TechArticle”,
“mainEntityOfPage”: {
“@type”: “WebPage”,
“@id”: “https://www.freedeets.com/2026/09/soc-2-audit-preparation-checklist-guide.html”
},
“headline”: “How to Prepare for a SOC 2 Audit: 7-Step Small Business Checklist (2026)”,
“description”: “A comprehensive 7-step operational checklist for small businesses and SaaS startups to prepare for SOC 2 Type I and Type II audits efficiently.”,
“image”: [
“https://freedeets.com/wp-content/uploads/2026/10/1000341927.webp”
],
“datePublished”: “2026-09-04T08:00:00+00:00”,
“dateModified”: “2026-09-04T08:00:00+00:00”,
“author”: {
“@type”: “Person”,
“name”: “Richa M”,
“jobTitle”: “Founder & Lead Content Strategist”,
“url”: “https://www.freedeets.com/p/about-us.html”
},
“publisher”: {
“@type”: “Organization”,
“name”: “Free Deets”,
“url”: “https://www.freedeets.com”,
“logo”: {
“@type”: “ImageObject”,
“url”: “https://www.freedeets.com/favicon.ico”
}
},
“proficiencyLevel”: “Intermediate”,
“dependencies”: “AICPA SOC 2 Framework, Cloud Infrastructure Access, Endpoint Security Tools”,
“articleSection”: “Technology & Cyber Risk Strategy”,
“keywords”: “SOC 2 Audit Preparation Checklist, SOC 2 Type II compliance, SOC 2 cost for small business, SOC 2 trust service criteria, SOC 2 audit readiness”,
“wordCount”: “2250”,
“inLanguage”: “en-US”
}
.fd-article {
font-family: -apple-system, BlinkMacSystemFont, “Segoe UI”, Roboto, Helvetica, Arial, sans-serif;
color: #1e293b;
line-height: 1.8;
font-size: 16px;
max-width: 900px;
margin: 0 auto;
padding: 10px 0;
}
/* Article Images */
.fd-img-container {
text-align: center;
margin: 28px 0 34px;
}
.fd-img-container img {
display: block;
width: 100%;
max-width: 900px;
height: auto;
margin: 0 auto;
border-radius: 12px;
box-shadow: 0 5px 18px rgba(0,0,0,0.10);
}
.fd-img-caption {
font-size: 0.88rem;
color: #64748b;
margin-top: 9px;
line-height: 1.5;
}
/* Headings */
.fd-article h2 {
color: #0f172a !important;
font-size: 1.5rem !important;
margin-top: 38px !important;
margin-bottom: 18px !important;
padding-bottom: 8px;
border-bottom: 2px solid #e2e8f0;
font-weight: 700;
}
.fd-article h3 {
color: #2563eb !important;
font-size: 1.2rem !important;
margin-top: 22px !important;
margin-bottom: 10px !important;
font-weight: 600;
}
.fd-article p {
margin-bottom: 18px;
}
.fd-article a {
color: #2563eb;
text-decoration: underline;
font-weight: 500;
}
.fd-article a:hover {
color: #1d4ed8;
}
.fd-article ul {
padding-left: 22px;
margin-bottom: 20px;
}
.fd-article li {
margin-bottom: 8px;
}
/* Responsive Tables */
.fd-table-wrapper {
overflow-x: auto;
-webkit-overflow-scrolling: touch;
margin: 25px 0;
border-radius: 8px;
border: 1px solid #e2e8f0;
box-shadow: 0 2px 5px rgba(0,0,0,0.03);
}
.fd-table {
width: 100%;
min-width: 650px;
border-collapse: collapse;
background: #ffffff;
text-align: left;
font-size: 0.95rem;
}
.fd-table th {
background-color: #0f172a;
color: #ffffff;
padding: 12px 16px;
font-weight: 600;
}
.fd-table td {
padding: 12px 16px;
border-bottom: 1px solid #e2e8f0;
vertical-align: top;
}
.fd-table tr:nth-child(even) {
background-color: #f8fafc;
}
/* Timeline */
.fd-timeline {
display: flex;
flex-direction: column;
gap: 18px;
margin: 25px 0;
}
.fd-step {
border: 1px solid #e2e8f0;
border-left: 5px solid #2563eb;
border-radius: 8px;
padding: 20px;
background: #ffffff;
}
.fd-badge {
display: inline-block;
background: #eff6ff;
color: #2563eb;
font-weight: 700;
font-size: 0.8rem;
padding: 3px 10px;
border-radius: 15px;
margin-bottom: 8px;
text-transform: uppercase;
}
.fd-step h3 {
margin: 0 0 10px 0 !important;
color: #0f172a !important;
}
/* Policy Grid */
.fd-grid {
display: grid;
grid-template-columns: repeat(auto-fit, minmax(250px, 1fr));
gap: 16px;
margin: 25px 0;
}
.fd-card {
background: #f8fafc;
border: 1px solid #e2e8f0;
border-radius: 8px;
padding: 18px;
}
.fd-card h4 {
color: #0f172a;
margin: 0 0 8px 0;
font-size: 1.05rem;
font-weight: 600;
}
.fd-card p {
font-size: 0.92rem;
margin: 0;
}
/* Information Box */
.fd-info {
background: #eff6ff;
border-left: 4px solid #2563eb;
padding: 16px 20px;
border-radius: 0 8px 8px 0;
margin: 20px 0;
color: #1e3a8a;
}
.fd-info p {
margin: 0;
}
/* Warning Box */
.fd-warning {
background: #fef2f2;
border-left: 4px solid #ef4444;
padding: 18px 20px;
border-radius: 0 8px 8px 0;
margin: 20px 0;
}
.fd-warning h4 {
color: #991b1b;
margin: 0 0 10px 0;
}
.fd-warning ul {
margin: 0;
color: #7f1d1d;
}
/* Mobile Optimization */
@media (max-width: 600px) {
.fd-article {
font-size: 15.5px;
line-height: 1.75;
padding: 5px 0;
}
.fd-article h2 {
font-size: 1.3rem !important;
line-height: 1.4 !important;
margin-top: 30px !important;
}
.fd-article h3 {
font-size: 1.1rem !important;
}
.fd-img-container {
margin: 22px 0 28px;
}
.fd-img-container img {
border-radius: 8px;
}
.fd-step {
padding: 16px;
}
.fd-grid {
grid-template-columns: 1fr;
}
.fd-table-wrapper {
margin-left: -2px;
margin-right: -2px;
}
}
In the contemporary enterprise technology landscape, demonstrating operational security is no longer restricted to Fortune 500 corporations. For small-to-medium-sized businesses (SMBs), business-to-business (B2B) Software-as-a-Service (SaaS) providers, and managed service vendors, securing a System and Organization Controls (SOC) 2 report has transitioned from a competitive advantage into a mandatory requirement for closing commercial contracts.
When prospective enterprise clients evaluate technology vendors, their primary concern centers on data security and operational resilience. An unverified infrastructure introduces substantial third-party risk. Obtaining a SOC 2 report provides evidence that an organization maintains controls governing data protection, system availability, processing integrity, confidentiality, and privacy.
However, navigating a SOC 2 audit can present significant financial and operational hurdles for smaller organizations with limited dedicated compliance resources. Without a structured preparation blueprint, SMBs risk prolonged audit timelines, unexpected remediation expenses, and operational disruption. This comprehensive guide delivers a step-by-step, 7-phase operational checklist tailored for small business leadership.
Understanding the Basics: SOC 2 Type I vs. SOC 2 Type II
Before initiating audit preparation, business leadership must differentiate between the two distinct reporting formats defined by the American Institute of Certified Public Accountants (AICPA).
| Evaluation Parameter | SOC 2 Type I Report | SOC 2 Type II Report |
|---|---|---|
| Primary Scope | Evaluates design suitability of controls at a single point in time. | Evaluates design suitability and operational effectiveness over a continuous tracking window. |
| Tracking Duration | Single date, such as December 31. | Continuous monitoring window, commonly 3, 6, or 12 months. |
| Preparation Timeline | Often shorter than Type II because there is no operating-effectiveness observation period. | Usually requires additional preparation and an operating period before testing is completed. |
| Primary Use Case | Organizations needing an assessment of control design at a defined date. | Organizations needing evidence that controls operated effectively over a period of time. |
| Audit Cost | Generally lower than a comparable Type II engagement. | Generally higher because testing covers an operating period and more evidence. |
Strategic Insight: A Type I report can provide an earlier assessment of control design, while a Type II report provides evidence about operating effectiveness over a defined period. The appropriate report depends on customer requirements, business risk, and audit objectives.
The 5 AICPA Trust Services Criteria (TSC) Explained
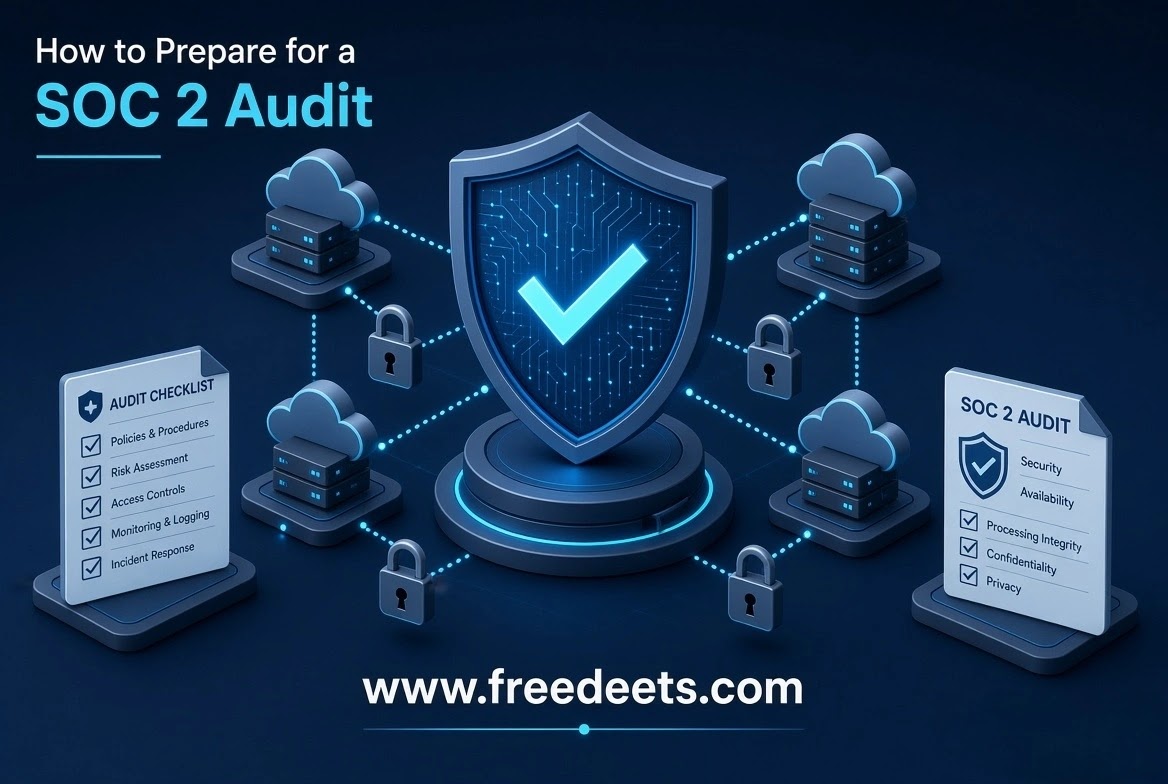
SOC 2 audits are framed around five Trust Services Criteria established by the AICPA Assurance Services Executive Committee. Security is the common criterion addressed in every SOC 2 examination. Availability, Processing Integrity, Confidentiality, and Privacy may be included when they are relevant to the organization’s services and commitments.
1. Security (Common Criteria)
Protecting systems and data against unauthorized physical and logical access. Core controls can include firewalls, multi-factor authentication (MFA), intrusion detection systems (IDS), web application firewalls (WAF), network segmentation, vulnerability management, and security monitoring. The NIST Cybersecurity Framework can also provide useful security-management guidance.
2. Availability
Ensuring operational infrastructure and application environments remain accessible and performant according to customer Service Level Agreements (SLAs). This criterion can be particularly relevant for hosting providers, cloud infrastructure services, and high-availability SaaS platforms.
3. Confidentiality
Protecting information designated as confidential from unauthorized disclosure throughout its lifecycle. This can be important for financial platforms, legal technology products, and businesses storing customer intellectual property.
4. Processing Integrity
Ensuring system processing is complete, valid, accurate, timely, and authorized. This can be critical for e-commerce platforms, fintech applications, automated transaction systems, and analytics services.
5. Privacy
Addressing the collection, use, retention, disclosure, and disposal of personally identifiable information (PII) in accordance with applicable privacy commitments and requirements. Organizations handling substantial amounts of customer PII should evaluate whether Privacy belongs within their SOC 2 scope.
The 7-Step SOC 2 Preparation Checklist for SMBs
Define Audit Scope & Select Applicable TSCs
- Determine Infrastructure Boundaries: Specify whether the audit applies to your entire hosting infrastructure or selected systems and services.
- Select Applicable Criteria: Evaluate customer contracts, services, risks, and commitments to determine whether Availability, Confidentiality, Processing Integrity, or Privacy should be included alongside Security.
- Exclude Non-Essential Systems: Clearly document systems that fall outside the audit boundary, such as certain development or staging environments, when justified.
Establish Internal Leadership & Team Accountability
- Appoint an Internal Compliance Owner: Designate a technical or operational lead to oversee project management and evidence collection.
- Engage Legal and HR Stakeholders: Assign responsible personnel to oversee background checks, acceptable-use acknowledgments, security awareness training, and employee lifecycle controls.
- Brief Executive Sponsors: Ensure company leadership understands the expected compliance investment, technology requirements, remediation work, and audit fees.
Conduct a Gap Analysis Against AICPA Criteria
- Review Existing Policies: Determine whether formal policies exist for information security, access control, password management, business continuity, change management, and incident response.
- Evaluate Infrastructure Security: Review user access rights across production databases, cloud management consoles, code repositories, identity providers, and other critical systems.
- Map Existing Controls to TSCs: Document how existing controls address applicable criteria and identify gaps requiring remediation.
Implement Operational & Technical Remediation
- Enforce Multi-Factor Authentication (MFA): Require strong MFA across corporate applications, email, cloud infrastructure, and other critical systems.
- Strengthen Endpoint Security: Use endpoint management capabilities to enforce encryption, screen-lock policies, patching, and device security requirements.
- Establish Centralized Logging & Monitoring: Collect relevant system and security logs and establish appropriate retention and monitoring procedures.
- Perform Independent Penetration Testing: Where appropriate, arrange independent security testing of external application infrastructure and remediate significant findings.
Deploy Compliance Automation Infrastructure
- Connect Evidence Sources: Integrate appropriate compliance tools with cloud providers, code repositories, task management platforms, HR systems, and identity systems.
- Establish Drift Detection: Configure alerts for important control deviations, such as improperly configured cloud storage or changes to security settings.
- Store Policy Acknowledgments: Maintain reliable records of employee policy acknowledgments and security-awareness activities.
Engage an Independent Licensed CPA Auditor
- Request Proposals from Multiple Firms: Compare experienced SOC 2 audit firms and evaluate their experience with SaaS companies and organizations of similar size.
- Confirm Audit Firm Reputation: Determine whether the firm’s reports meet the expectations of important customers and procurement teams.
- Establish Pre-Audit Readiness: Conduct a readiness assessment or dry run before the formal audit period where appropriate.
Complete the Audit Tracking Period & Manage Results
- Execute Type I or Type II Assessment: For Type I, the auditor evaluates controls at a specified point in time. For Type II, the auditor evaluates control operation over a defined period.
- Fulfill Evidence Requests: Provide relevant access reviews, employee onboarding and offboarding records, change-management records, security monitoring evidence, training records, and other requested documentation.
- Review the Final Report: Work with the audit firm through the final reporting process and carefully review any exceptions or findings.
Core Security Policies Required for SOC 2
To achieve audit readiness, organizations should document and maintain a foundational set of security policies. Auditors evaluate whether relevant policies and controls are established, communicated, implemented, and supported by evidence.
Master Information Security Policy
Defines the organization’s overarching security commitments, responsibilities, risk management approach, and enforcement framework.
Access Control Policy
Defines authentication requirements, least-privilege access, MFA, access reviews, provisioning, and employee offboarding procedures.
Change Management Policy
Defines code review, testing, approvals, deployment, documentation, and change-control requirements.
Incident Response Plan
Establishes incident severity levels, escalation channels, containment procedures, investigation processes, and post-incident review activities.
Disaster Recovery & Business Continuity
Documents recovery objectives, backup procedures, recovery testing, communication processes, and business continuity responsibilities.
Vendor Risk Management Policy
Establishes vendor onboarding reviews, risk assessments, contractual requirements, monitoring, and evidence collection for critical third parties.
Total Cost Breakdown: SOC 2 Budget Expectations for SMBs
Budgeting for SOC 2 requires planning for both direct audit expenses and the internal operational effort required to establish and maintain effective controls. Actual costs vary considerably according to company size, audit scope, technology environment, readiness, and selected service providers.
| Expense Category | Typical Vendor / Service | Illustrative Cost Range (USD) |
|---|---|---|
| Licensed CPA Audit Firm | Independent CPA Firm | Varies by scope and engagement |
| Compliance Automation Software | Continuous Monitoring Platform | Varies by provider and company size |
| Third-Party Penetration Test | External Cybersecurity Testing Firm | Varies by application scope |
| Endpoint Management | Device Security / MDM Platform | Varies by users and platform |
| Employee Background Checks | Screening Provider | Varies by jurisdiction and provider |
| Internal Engineering Time | Security, DevOps and Compliance Work | Depends on readiness and scope |
Common Pitfalls That Delay SOC 2 Audits
- Inconsistent Employee Offboarding: Failing to promptly revoke access after termination can create an audit exception.
- Unverified Change Management Records: Production changes without documented approvals, reviews, testing, or deployment records can create evidence gaps.
- Unperformed Periodic Reviews: Missing security training, access reviews, incident-response exercises, or vendor reviews can weaken the evidence trail.
- Ad-Hoc Access Provisioning: Permanent administrator privileges granted for temporary tasks can conflict with least-privilege principles.
Key Action Items to Begin Your SOC 2 Journey
Achieving SOC 2 readiness is a significant operational milestone that can help organizations demonstrate a structured approach to security and support enterprise customer due-diligence processes.
- Formally define your audit scope and determine which Trust Services Criteria apply.
- Conduct an internal gap analysis to identify missing controls and documentation.
- Deploy appropriate compliance and evidence-management tools early enough to establish reliable records.
- Establish written security policies and enforce strong authentication and access controls.
- Maintain consistent evidence throughout the relevant audit period.
- Engage an experienced licensed CPA firm that is appropriate for your organization’s scope and requirements.